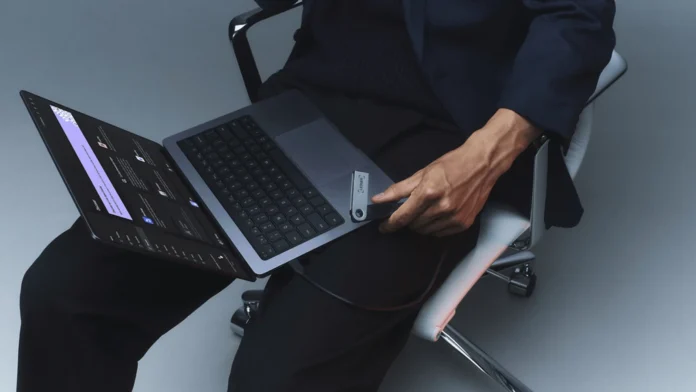

Hardware wallet manufacturer Ledger has announced it is currently investigating the loss of user funds after several customers located in Southeast Asia reported problems involving devices purchased through a reseller.
On Friday, the Paris-headquartered firm issued a warning advising anyone who bought a device from the vendor CryptoBilis over the past 90 days to refrain from setting it up.
While Ledger did not disclose the precise financial losses suffered by users, a blockchain investigator known as Specter shared on X that, after tracking theft addresses following various social media reports, more than $86 million appeared to have been lost.
This development follows a series of cryptocurrency data breaches throughout the year, alongside a massive hack affecting popular Coldcard hardware wallets back in July.
“Ledger is investigating reports of loss of funds from users in South East Asia who purchased products from a reseller named CryptoBilis,” the company stated via its official support account on X.
Ledger further noted that it has instructed CryptoBilis to immediately halt all sales and shipments of Ledger-branded hardware.
“If you have set up your Ledger device, consider moving assets to a new Ledger signer (with new seed). We will continue to inform customers of updates as the investigation progresses,” the company advised.
In a statement provided to Bitcoin Magazine, Ledger emphasized that current information indicates the incident is isolated strictly to this specific reseller within that regional market.
“No reports were made of products purchased directly from Ledger, and Ledger’s infrastructure, systems and services were not compromised,” the manufacturer added.
Website details indicate that CryptoBilis is a hardware wallet vendor situated in Kuala Lumpur, Malaysia. The firm did not immediately reply to inquiries from Bitcoin Magazine.
The wider crypto sector continues to recover from a July incident where hackers managed to siphon nearly $120 million worth of bitcoin from Coldcard users.
Those items, manufactured by the Canadian firm Coinkite, suffered from a firmware flaw that caused faulty seed generation, empowering malicious actors to accurately guess investor seed phrases.
According to Galaxy Research, multiple independent attackers successfully exploited that vulnerability in the aftermath of the initial breach.
In an unrelated event last month, rival hardware wallet maker Trezor disclosed that the personal information of nearly 81,000 customers was exposed after a data breach hit its third-party fulfillment partner.
Bad actors have heavily targeted customer data throughout the year, including an incident where scammers obtained consumer details through Ledger’s payment processor, Global-e, to launch targeted phishing emails.
Frequently Asked Questions
What did Ledger advise customers who bought from CryptoBilis to do?
Ledger advised customers who purchased devices from CryptoBilis within the last 90 days not to set them up, and recommended that anyone who already set up their device should transfer their assets to a new Ledger signer using a fresh seed.
How much money was allegedly lost in the incident?
Ledger did not officially disclose the total amount lost, but a blockchain investigator named Specter stated on X that he traced theft addresses and calculated losses exceeding $86 million.
Was Ledger’s own infrastructure compromised?
No, Ledger stated that its infrastructure, systems, and services were not compromised, and that no reports involved products bought directly from Ledger.
Who is CryptoBilis?
CryptoBilis is a hardware wallet vendor located in Kuala Lumpur, Malaysia, which Ledger has asked to pause all sales and shipments of Ledger devices.